ISO 27001 Certification in North Macedonia
ISO 27001 Certification in North Macedonia helps organizations establish an effective Information Security Management System (ISMS) to protect sensitive information, reduce cybersecurity risks, and strengthen business resilience.
As North Macedonia’s technology, banking, healthcare, telecommunications, manufacturing, logistics, government, energy, and digital service sectors increasingly rely on information systems and cloud technologies, effective information security has become essential. ISO 27001 provides an internationally recognized framework for identifying security risks, implementing appropriate controls, and protecting information assets.
What is ISO 27001 Certification?
ISO 27001 is an internationally recognized standard for Information Security Management Systems. It helps organizations identify threats, assess information security risks, implement suitable controls, and continually improve their security management practices.
Certification demonstrates that an organization has established a structured approach to protecting confidential information, maintaining data integrity, ensuring information availability, and managing cybersecurity risks.
Our ISO 27001 Certification Process
Our ISO 27001 certification process begins with an assessment of your existing information security practices, IT infrastructure, business processes, and risk management controls. We then conduct a detailed gap analysis against ISO 27001 requirements to identify vulnerabilities and areas requiring improvement.
Our consultants develop information security policies, risk assessment procedures, risk treatment plans, access control processes, incident response procedures, asset management controls, business continuity arrangements, and supporting documentation required for an effective ISMS.
The Information Security Management System is then implemented throughout relevant business operations. Employees receive practical training on information security awareness, data protection, access management, incident reporting, and their ISO 27001 responsibilities.
Following implementation, internal audits and management reviews verify compliance, assess control effectiveness, and identify corrective actions. We provide complete support throughout the external certification audit and assist with addressing findings until your organization successfully achieves ISO 27001 certification.
Benefits of ISO 27001 Certification in North Macedonia
- Protects confidential business information
- Reduces cybersecurity risks
- Strengthens information security controls
- Enhances customer confidence
- Supports regulatory compliance
- Improves risk management
- Strengthens business continuity
- Promotes continual improvement
Who Needs ISO 27001 Certification?
ISO 27001 is suitable for organizations that collect, process, store, or manage sensitive information.
Technology companies use it to protect customer data and strengthen cybersecurity. Financial institutions implement it to manage information security risks and protect sensitive financial information.
It is also beneficial for healthcare organizations, telecommunications providers, software companies, cloud service providers, manufacturing businesses, logistics organizations, government agencies, educational institutions, energy companies, and professional service providers.
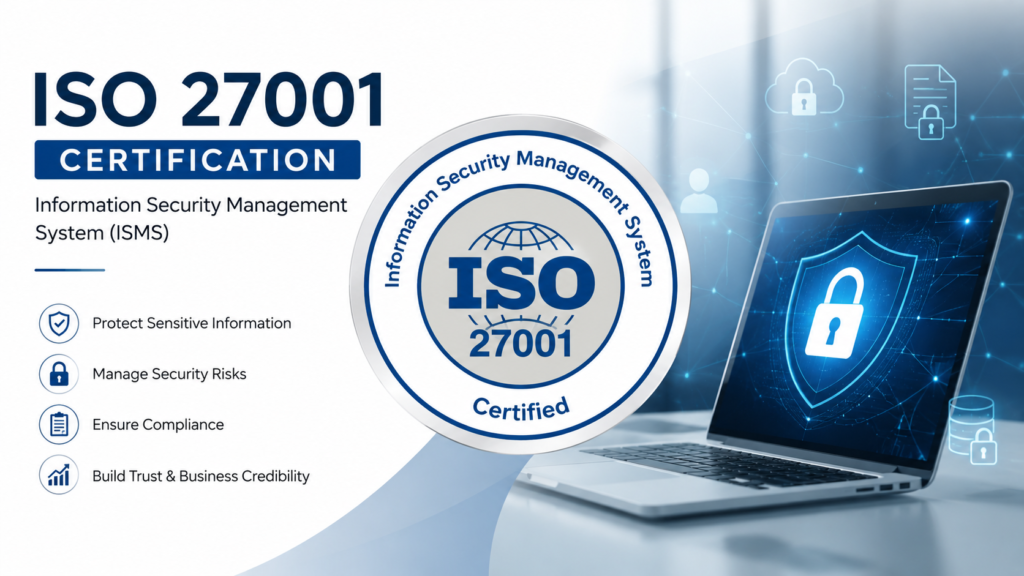
Why ISO 27001 Matters in North Macedonia?
Organizations in North Macedonia increasingly depend on digital systems, online services, cloud platforms, and interconnected infrastructure. Protecting information from unauthorized access, loss, or disruption is therefore an important business priority.
ISO 27001 helps organizations strengthen cybersecurity, improve risk management, reduce security incidents, and demonstrate internationally recognized information security management practices to customers and business partners.
Why Choose Us?
We provide customized ISO 27001 consulting services tailored to your organization’s information security objectives, operational environment, and industry requirements.
Our experienced consultants support implementation, documentation, risk assessment, employee training, internal audits, corrective actions, and certification audit preparation to ensure a smooth and successful certification process.
Contact our experts today to begin your ISO 27001 certification journey in North Macedonia.
LIMITED TIME OFFER
Get Your Custom Quote Today
Fill out the form to unlock your exclusive pricing and rapid implementation plan.
- Transparent Pricing
- No Hidden Fees
- Full Documentation Support
- Audit Preparation Included
Our Proven Path to ISO 27001 Certification
Our streamlined process ensures a clear and efficient path to your certification with minimal ISO certification cost.
1
We start by understanding your business, processes, and objectives to define the scope of your QMS.
2
We assist in developing all necessary QMS documentation and guide you through implementing the new processes.
3
We coordinate with an accredited certification body for your Stage 1 and Stage 2 audits.
4
Our experts conduct a thorough assessment of your existing systems against ISO 9001 requirements to identify gaps.
5
We conduct an internal audit to ensure readiness and facilitate the management review meeting.
Get Certified!
Receive your official ISO 9001 Quality Management certificate and leverage your new competitive advantage.

Why Choose Isomark Global?
We make ISO certification simple, secure, and efficient.
Expert ISO 27001 Consultants
Experienced professionals in cybersecurity and compliance.
Fast Certification Support
Efficient processes for faster certification timelines.
Complete Documentation Assistance
Full ISMS documentation and implementation support.
Audit Preparation
Ensure confidence and readiness for certification audits.
Affordable Pricing
Transparent pricing with no hidden costs.
Ongoing Compliance Support
Continuous support to maintain ISO 27001 compliance.
ISO 27001 Certification FAQs
What is ISO 27001 Certification?
ISO 27001 is an international standard for Information Security Management Systems that helps organizations protect information assets and manage security risks.
Is ISO 27001 mandatory in North Macedonia?
No. ISO 27001 is voluntary, but many organizations implement it to strengthen information security and meet customer or contractual requirements.
Who should implement ISO 27001?
Organizations that manage sensitive, confidential, or critical information should implement ISO 27001.
What is the main objective of ISO 27001?
The main objective is to establish an effective Information Security Management System that protects information assets, manages security risks, and supports continual improvement.