ISO 27001 Certification in Slovakia
ISO 27001 Certification in Slovakia helps organizations establish an effective Information Security Management System (ISMS) to protect sensitive information, manage cybersecurity risks, and strengthen business resilience.
As Slovakia’s automotive, manufacturing, technology, banking, healthcare, telecommunications, logistics, energy, and digital service sectors increasingly depend on information systems and cloud technologies, strong information security has become essential. ISO 27001 provides an internationally recognized framework for identifying risks, implementing appropriate security controls, and protecting valuable information assets.
What is ISO 27001 Certification?
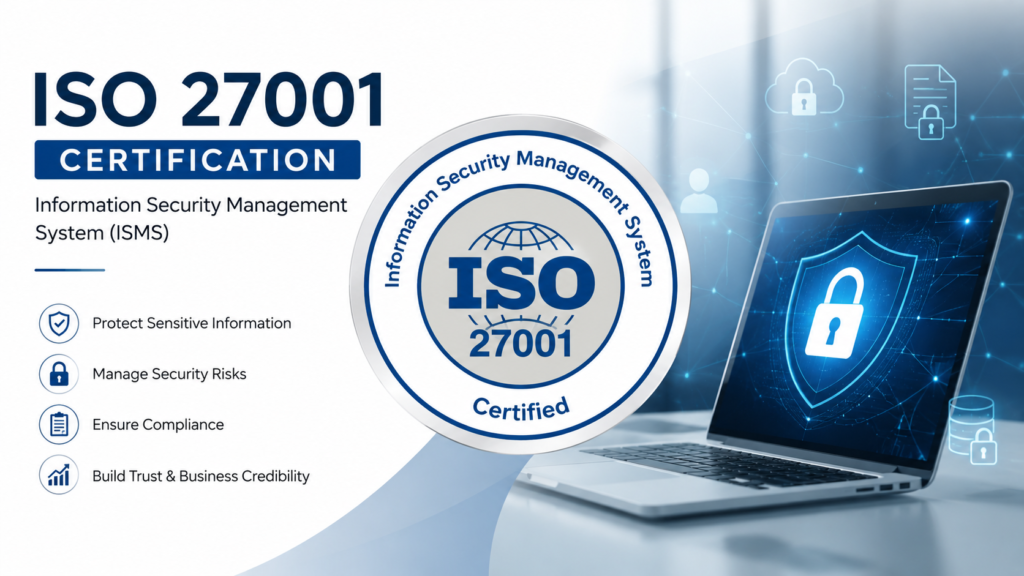
ISO 27001 is an internationally recognized standard for Information Security Management Systems. It helps organizations identify security threats, assess risks, implement effective security controls, and continually improve information security performance.
Certification demonstrates that an organization has established a structured system to protect confidential information, maintain data integrity, ensure information availability, and manage cybersecurity risks effectively.
Our ISO 27001 Certification Process
Our ISO 27001 certification process begins with an assessment of your existing information security practices, IT infrastructure, business processes, and security controls. We then conduct a detailed gap analysis against ISO 27001 requirements to identify vulnerabilities, compliance gaps, and improvement opportunities.
Our consultants develop information security policies, risk assessment procedures, risk treatment plans, asset management controls, access control procedures, incident response processes, business continuity arrangements, and supporting documentation required for an effective ISMS.
The Information Security Management System is then implemented throughout relevant business operations. Employees receive practical training on information security awareness, secure data handling, access management, incident reporting, and ISO 27001 responsibilities.
Following implementation, internal audits and management reviews verify compliance, evaluate control effectiveness, and identify corrective actions. We provide complete support throughout the external certification audit and assist with addressing findings until your organization successfully achieves ISO 27001 certification.
Benefits of ISO 27001 Certification in Slovakia
- Protects confidential business information
- Reduces cybersecurity risks
- Strengthens information security controls
- Improves data protection practices
- Enhances customer confidence
- Supports regulatory compliance
- Strengthens risk management
- Improves business continuity
- Promotes continual improvement
Who Needs ISO 27001 Certification?
ISO 27001 is suitable for organizations that collect, process, store, or manage sensitive information.
Technology companies use it to protect customer data and cloud-based systems. Financial institutions implement it to strengthen information security and protect sensitive financial information.
It is also beneficial for healthcare providers, telecommunications companies, software businesses, manufacturing organizations, logistics providers, government agencies, educational institutions, energy companies, cloud service providers, and professional service organizations.
Why ISO 27001 Matters in Slovakia?
Slovakia’s highly connected economy and integration with European and international supply chains make information security an important business priority.
Organizations increasingly depend on digital platforms, cloud services, connected systems, and electronic data. ISO 27001 helps businesses strengthen cybersecurity, improve risk management, reduce security incidents, and demonstrate internationally recognized information security practices.
Why Choose Us?
We provide customized ISO 27001 consulting services tailored to your organization’s information security objectives, operational environment, and industry requirements.
Our experienced consultants support implementation, documentation, risk assessment, employee training, internal audits, corrective actions, and certification audit preparation to ensure a smooth and successful certification process.
Contact our experts today to begin your ISO 27001 certification journey in Slovakia.
LIMITED TIME OFFER
Get Your Custom Quote Today
Fill out the form to unlock your exclusive pricing and rapid implementation plan.
- Transparent Pricing
- No Hidden Fees
- Full Documentation Support
- Audit Preparation Included
Our Proven Path to ISO 27001 Certification
Our streamlined process ensures a clear and efficient path to your certification with minimal ISO certification cost.
1
We start by understanding your business, processes, and objectives to define the scope of your QMS.
2
We assist in developing all necessary QMS documentation and guide you through implementing the new processes.
3
We coordinate with an accredited certification body for your Stage 1 and Stage 2 audits.
4
Our experts conduct a thorough assessment of your existing systems against ISO 9001 requirements to identify gaps.
5
We conduct an internal audit to ensure readiness and facilitate the management review meeting.
Get Certified!
Receive your official ISO 9001 Quality Management certificate and leverage your new competitive advantage.

Why Choose Isomark Global?
We make ISO certification simple, secure, and efficient.
Expert ISO 27001 Consultants
Experienced professionals in cybersecurity and compliance.
Fast Certification Support
Efficient processes for faster certification timelines.
Complete Documentation Assistance
Full ISMS documentation and implementation support.
Audit Preparation
Ensure confidence and readiness for certification audits.
Affordable Pricing
Transparent pricing with no hidden costs.
Ongoing Compliance Support
Continuous support to maintain ISO 27001 compliance.
ISO 27001 Certification FAQs
What is ISO 27001 Certification?
ISO 27001 is an international standard for Information Security Management Systems that helps organizations protect information assets and manage security risks.
Is ISO 27001 mandatory in Slovakia?
No. ISO 27001 is voluntary, but many organizations implement it to strengthen information security and meet customer, contractual, or supply chain requirements.
Who should implement ISO 27001?
Organizations that manage sensitive, confidential, or critical information should implement ISO 27001.
What is the main objective of ISO 27001?
The main objective is to establish an effective Information Security Management System that protects information assets, manages security risks, and supports continual improvement.